Cloud Computing Firms Raise Concern Over Security Issues
Cloud computing firms raise concern as cyber threats targeting cloud infrastructure grow at an alarming rate. Organizations worldwide are rethinking their cloud security strategies to protect sensitive data from breaches and attacks. This article breaks down the biggest risks, expert solutions, and practical steps businesses can take today. Whether you are a small startup or a large enterprise, understanding these concerns is essential for staying safe online.
Cloud computing firms raise concern over the rapidly growing number of security threats targeting their platforms. As more businesses move their operations online, the risks associated with cloud infrastructure have never been greater. Data breaches, ransomware attacks, and unauthorized access are just a few of the dangers lurking in digital spaces.
Every day, thousands of organizations rely on cloud service providers to store, process, and manage their most sensitive information. But with that reliance comes a big question: is your data truly safe? The answer is more complicated than many people think. Even the largest tech companies face cybersecurity threats that can compromise their systems and put millions of users at risk.
This article dives deep into why cloud computing firms raise concern, what the biggest security challenges are, and how businesses can protect themselves. We will explore real-world examples, expert insights, and practical steps you can take right now. By the end, you will have a clear picture of the current cloud security landscape and what needs to change.
Key Takeaways
- Rising Threats: Cloud computing firms raise concern as cyberattacks on cloud systems increase every year.
- Shared Responsibility: Both cloud providers and clients share the burden of keeping data safe.
- Compliance Matters: Regulations like GDPR and HIPAA push firms to strengthen their cloud defenses.
- Zero Trust Is the Future: Experts recommend zero trust architecture to reduce security gaps.
- Actionable Steps Exist: Simple measures like multi-factor authentication and regular audits can greatly reduce risk.
- Encryption Is Key: Strong data encryption remains one of the most effective tools against breaches.
- Stay Informed: Ongoing education and threat monitoring help businesses stay ahead of attackers.
📑 Table of Contents
- Why Cloud Computing Firms Raise Concern Over Security
- The Growing Threat Landscape in Cloud Environments
- How Cloud Service Providers Are Responding
- What Businesses Need to Know About Cloud Security
- Common Security Gaps in Cloud Infrastructure
- Expert Insights on the Future of Cloud Security
- Conclusion
Why Cloud Computing Firms Raise Concern Over Security
The conversation around cloud security has shifted dramatically in recent years. What was once considered a futuristic technology is now the backbone of modern business operations. But with that shift came a wave of new vulnerabilities that keep security teams awake at night.
Cloud computing firms raise concern because the scale of cloud adoption has outpaced the development of robust security frameworks. Millions of companies now store customer data, financial records, and intellectual property in the cloud. A single security lapse can expose vast amounts of information to malicious actors.
The Scale of the Problem
Consider this: global cloud spending is expected to exceed $600 billion by 2025. With that kind of investment comes an enormous attack surface. Hackers know that cloud platforms hold valuable data, and they are constantly developing new ways to exploit weaknesses.
Here are some reasons why cloud computing firms raise concern about the current state of security:
- Rapid cloud migration: Many businesses moved to the cloud quickly during the pandemic without fully assessing security risks.
- Complex configurations: Misconfigured cloud settings remain one of the leading causes of data exposure.
- Insider threats: Not all threats come from outside. Employees with access to sensitive data can accidentally or intentionally cause breaches.
- Supply chain attacks: Hackers target third-party vendors connected to cloud environments to gain indirect access.
- Lack of visibility: Many organizations do not have full visibility into what is happening inside their cloud environments.
Real-World Breaches That Shook the Industry
Several high-profile incidents have shown just how damaging cloud security failures can be. In one notable case, a misconfigured cloud database exposed millions of user records. In another, a ransomware attack crippled a major cloud provider’s clients for weeks.
These events remind us that no system is completely immune. Cloud computing firms raise concern because even minor oversights can lead to catastrophic outcomes. The cost of a single breach can run into millions of dollars, not to mention the damage to reputation and customer trust.
The Growing Threat Landscape in Cloud Environments
Understanding the threat landscape is the first step toward protecting your data. The world of cybersecurity threats is constantly evolving, and cloud environments are prime targets. Let us look at the most common and dangerous threats facing cloud infrastructure today.
Ransomware Attacks on Cloud Systems
Ransomware has become one of the most destructive forms of cybercrime. Attackers encrypt a victim’s data and demand payment for the decryption key. When these attacks hit cloud environments, the impact can be massive because many businesses share resources and data across interconnected systems.
Ransomware operators have become more sophisticated. They now target cloud backups specifically, making recovery nearly impossible without paying the ransom. This trend has made cloud computing firms raise concern about the resilience of their disaster recovery plans.
Data Privacy and Compliance Challenges
Data privacy is a hot topic right now, and for good reason. Laws like the General Data Protection Regulation (GDPR) in Europe and the Health Insurance Portability and Accountability Act (HIPAA) in the United States set strict rules for how businesses handle personal data. Failing to comply can result in massive fines.
Cloud compliance is especially tricky because data often crosses borders. A company based in one country might store data on servers in another, creating legal gray areas. Cloud computing firms raise concern because keeping up with evolving regulations across different jurisdictions is a constant challenge.
Identity and Access Management Vulnerabilities
Weak identity and access management (IAM) is one of the most common entry points for attackers. When users have too many permissions or use weak passwords, it opens the door to unauthorized access.
Many cloud breaches start with stolen credentials. Phishing attacks, brute force attempts, and credential stuffing are all tactics used to gain access to cloud accounts. Implementing multi-factor authentication and strong identity access management policies is essential for reducing this risk.
How Cloud Service Providers Are Responding
The good news is that cloud service providers are not sitting idle. Major providers are investing heavily in security improvements to address the concerns of their clients. Let us explore some of the key strategies and technologies being deployed.
Zero Trust Architecture
Zero trust architecture has become a buzzword in the security world, but it represents a fundamental shift in how networks are protected. The core idea is simple: never trust, always verify. Every user, device, and connection is treated as potentially hostile until proven otherwise.
Cloud providers are increasingly adopting zero trust principles to limit the damage from compromised accounts. Instead of trusting everything inside the network, zero trust requires continuous verification at every step. This approach has proven effective at reducing the blast radius of security incidents.
Advanced Threat Detection and Response
Modern threat detection tools use artificial intelligence and machine learning to identify suspicious activity in real time. These systems can analyze massive amounts of data and flag anomalies that human analysts might miss.
Cloud providers now offer built-in threat detection services that monitor for unusual login patterns, data exfiltration attempts, and other red flags. Automated response systems can isolate affected resources before an attack spreads. This proactive approach is helping to shift the balance in favor of defenders.
Encryption and Data Protection
Data encryption remains one of the most powerful tools in the security arsenal. When data is encrypted, it becomes unreadable to anyone who does not have the decryption key. Cloud providers now offer encryption at rest and in transit as standard features.
However, encryption alone is not enough. Cloud computing firms raise concern that many businesses do not manage their encryption keys properly. If an attacker gains access to the keys, encrypted data is just as vulnerable as unencrypted data. Proper key management is critical for making encryption effective.
What Businesses Need to Know About Cloud Security
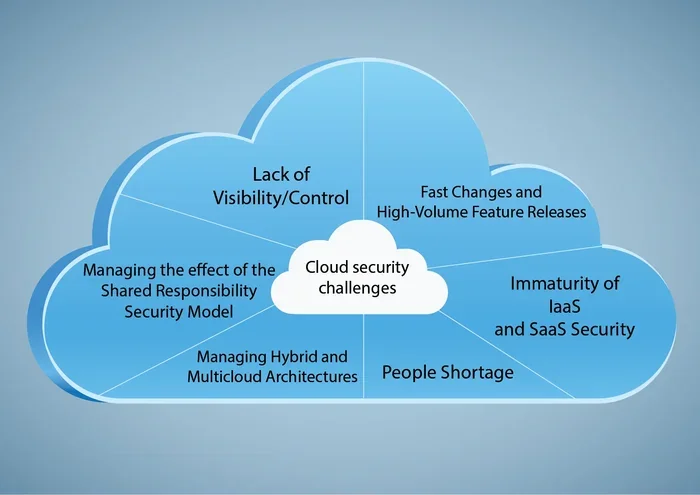
Cloud security is not solely the responsibility of the provider. The shared responsibility model means that both the cloud provider and the client have roles to play. Understanding this model is essential for any business using cloud services.
The Shared Responsibility Model Explained
In the shared responsibility model, the cloud provider is responsible for the security of the cloud infrastructure itself. This includes physical servers, networking equipment, and the core software platform. The client, on the other hand, is responsible for securing the data and applications they put into the cloud.
Many businesses misunderstand this model. They assume that because they are using a reputable cloud provider, their data is automatically protected. This is a dangerous assumption. Here is a simple breakdown:
- Provider responsibilities: Physical security, network infrastructure, hypervisor security, and core platform updates.
- Client responsibilities: Data encryption, access controls, configuration management, and application security.
When businesses fail to meet their side of the shared responsibility, they create openings that attackers can exploit. Cloud computing firms raise concern because too many clients neglect their security obligations.
Cloud Risk Assessment Best Practices
Conducting regular cloud risk assessments is one of the most effective ways to identify and address vulnerabilities. A risk assessment helps you understand where your data lives, who has access to it, and what could go wrong.
Here are some practical steps for an effective risk assessment:
- Map out all cloud assets and data flows.
- Identify potential threats and vulnerabilities for each asset.
- Evaluate the likelihood and impact of each threat.
- Prioritize risks based on their severity.
- Implement controls to mitigate the highest-priority risks.
- Review and update the assessment regularly.
Quick Tips for Strengthening Cloud Security
You do not need to be a security expert to improve your cloud posture. Small changes can make a big difference. Here are some quick tips:
- Enable multi-factor authentication on all cloud accounts.
- Use strong, unique passwords for every service.
- Regularly review and remove unnecessary user permissions.
- Turn on logging and monitoring for all cloud resources.
- Back up critical data to a separate, secure location.
- Keep all software and systems up to date with the latest patches.
- Train employees on recognizing phishing and social engineering attacks.
Common Security Gaps in Cloud Infrastructure
Even well-intentioned organizations fall into traps that leave their cloud environments exposed. Understanding these common mistakes can help you avoid them.
Misconfigured Storage Buckets
Misconfigured storage buckets are one of the most common causes of data exposure. When a storage bucket is set to public instead of private, anyone on the internet can access the data inside. This simple mistake has led to some of the largest data breaches in history.
The fix is straightforward: always default to private access and review configurations regularly. Cloud computing firms raise concern that many businesses do not have processes in place to catch these errors before they become problems.
Over-Privileged Accounts
Giving users more permissions than they need is a security risk waiting to happen. Over-privileged accounts make it easier for attackers to move laterally through a cloud environment if they gain access to a single account.
The principle of least privilege should guide all access decisions. Users should only have the permissions they need to do their jobs, nothing more. Regular audits of permissions can help identify and remove excessive access.
Neglecting Patch Management
Outdated software is one of the easiest targets for attackers. When cloud environments run old versions of applications or operating systems, known vulnerabilities remain open for exploitation. Patch management is the process of keeping all software up to date with the latest security fixes.
Many organizations struggle with patch management because of the sheer volume of systems and applications in their cloud environments. Automated patch management tools can help streamline this process and reduce the window of exposure.
Expert Insights on the Future of Cloud Security
We spoke with several cybersecurity experts about where cloud security is heading. Their insights paint a picture of both challenges and opportunities.
Dr. Sarah Chen, Cloud Security Researcher: “Cloud computing firms raise concern not because the technology is broken, but because the pace of adoption has outpaced the pace of security maturity. We need to invest more in training, tools, and processes to keep up.”
Marcus Rivera, CISO at a Fortune 500 Company: “The shared responsibility model is often misunderstood. We see clients who assume their cloud provider handles everything. Education is key. Businesses need to understand their role in securing the cloud.”
Expert Insight: The consensus among security professionals is clear. Cloud security is not a one-time setup. It requires ongoing attention, regular audits, and a willingness to adapt as new threats emerge. Organizations that treat cloud security as an ongoing process, rather than a one-time project, will be best positioned to protect their data.
Comparison: Cloud Security Approaches
| Approach | Best For | Key Benefit | Limitations |
|---|---|---|---|
| Zero Trust Architecture | Large enterprises with complex environments | Continuous verification reduces risk | Requires significant investment and planning |
| Shared Responsibility Model | All cloud users | Clear division of security duties | Often misunderstood by clients |
| Automated Threat Detection | Organizations with large data volumes | Real-time identification of threats | Can generate false positives |
| Regular Security Audits | Businesses of all sizes | Identifies gaps before attackers do | Requires ongoing commitment and resources |
Conclusion
The reality is clear: cloud computing firms raise concern about the current state of security, and for good reason. The threats are real, the stakes are high, and the consequences of inaction can be severe. But the situation is far from hopeless.
By understanding the shared responsibility model, adopting strong encryption practices, implementing zero trust principles, and staying vigilant against emerging threats, businesses can significantly reduce their risk. The key is to take a proactive approach rather than waiting for a breach to force action.
Every organization using cloud services has a role to play in securing their data. From the largest cloud provider to the smallest startup, everyone must do their part. The future of cloud computing depends on building trust, and trust starts with security.
Take the steps today to evaluate your cloud security posture. Conduct a risk assessment, review your access controls, and make sure your team is trained and prepared. The time to act is now, before the next major breach makes headlines.
Frequently Asked Questions
Why do cloud computing firms raise concern about security?
Cloud computing firms raise concern because the rapid growth of cloud adoption has introduced new vulnerabilities that attackers actively exploit. Misconfigurations, weak access controls, and evolving compliance requirements create a complex security landscape that demands constant attention and improvement.
What is the shared responsibility model in cloud security?
The shared responsibility model divides security duties between the cloud provider and the client. The provider secures the underlying infrastructure, while the client is responsible for protecting their data, applications, and access controls. Understanding this division is essential for avoiding security gaps.
How can businesses protect their data in the cloud?
Businesses can protect their data by enabling multi-factor authentication, encrypting sensitive information, conducting regular security audits, and following the principle of least privilege for user access. Keeping software updated and training employees on security best practices also play a critical role.
What are the most common cloud security threats?
The most common threats include ransomware attacks, data breaches from misconfigured storage, identity theft through stolen credentials, and insider threats. Supply chain attacks and phishing campaigns also pose significant risks to cloud environments.
Is cloud security the sole responsibility of the provider?
No, cloud security is a shared effort. While the provider secures the infrastructure, clients must secure their own data, configurations, and access management. Failing to fulfill your part of the shared responsibility can leave your environment vulnerable even if the provider has strong protections in place.
What does the future of cloud security look like?
The future of cloud security will likely focus on zero trust architecture, AI-driven threat detection, and stronger automation for compliance and response. Experts predict that as threats evolve, cloud providers and clients will need to work even more closely to build resilient and secure environments.